CMMC Enclave for CMMC Compliance, Without an Enterprise Price Tag
Espresso Labs helps you stand up, manage, and monitor a CMMC enclave using GCC High, PreVeil, or the Espresso Labs enclave, and maps everything it does back to your CMMC compliance controls and evidence.
What Is a CMMC Enclave, and Do You Need One?
A CMMC enclave is a smaller, tightly controlled environment that isolates the systems handling Controlled Unclassified Information (CUI), so the rest of your company doesn't have to fall inside the scope of a CMMC compliance assessment. For organizations pursuing CMMC Level 2, a CMMC enclave is one of the most effective ways to protect CUI without bringing the entire company into scope.
Espresso Labs helps you stand up, manage, and monitor that CMMC enclave, using partner solutions or the Espresso Labs enclave, so you get real protection at a fraction of what enterprise-scale deployments typically cost.
How a CMMC Enclave Fits Into Your Environment
CUI stays isolated inside the enclave, reachable only through a secure remote connection. Espresso Labs Cloud manages and monitors that enclave from outside its boundary, so the environment holding your CUI stays exactly as tightly scoped as your assessment requires, without becoming something your team has to run day to day.
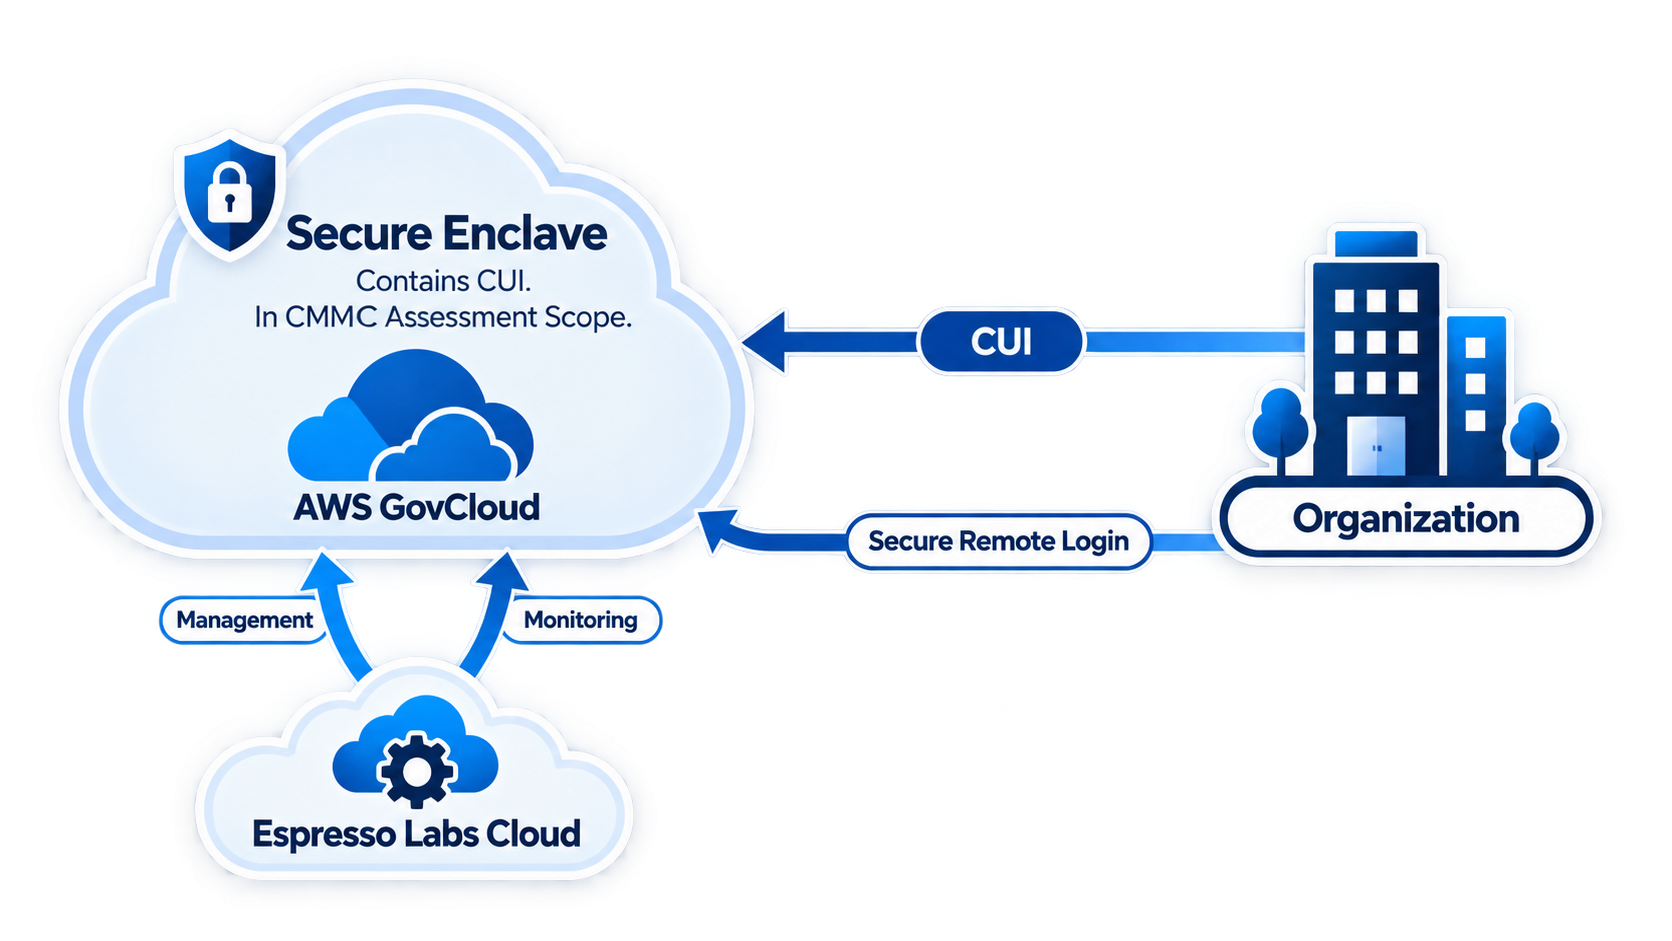
The Right Enclave for Your Organization
There's no single right answer for every organization. We help you choose and implement the option that fits your budget, your existing systems, and your CUI footprint:
GCC High
Microsoft's government community cloud environment, for organizations standardized on Microsoft 365.
PreVeil
End-to-end encrypted email and file sharing purpose-built for CUI, without the cost of a full GCC High migration.
Espresso Labs Enclave
A dedicated, isolated environment built on your existing infrastructure, scoped tightly to your CUI needs.
Whichever path fits, the goal is the same: protect CUI without forcing an expensive, disruptive overhaul of how your whole company works.
No VDI Required
Many enclave approaches lean on Virtual Desktop Infrastructure (VDI): every person who touches CUI gets a separate virtual desktop, and every day-to-day task happens inside it. VDI works, but it's expensive to license per seat, slow to roll out, and adds a layer of latency and friction your team feels every single day.
Espresso Labs' enclaves aren't VDI-based. Instead of routing your team through a virtual desktop, we focus on securing the CUI itself and controlling who and what can access it. That means the complexity and inefficiency VDI introduces, licensing overhead, remote desktop lag, a second toolchain to maintain, simply isn't part of the equation.
Fully Managed, Mapped to Your Controls
Standing up an enclave is only the first step. Espresso Labs manages and monitors it on your behalf, and connects it directly to your compliance program:
- ✓We configure, manage, and monitor the enclave on an ongoing basis, so it doesn't drift out of a secure state after launch.
- ✓Access, activity, and security events inside the enclave are mapped back to the specific controls they satisfy.
- ✓Evidence is collected automatically, so the enclave shows up in your GRC dashboard and audit record, not as a separate, disconnected system.
You get the scope-reduction benefits of an enclave without taking on a second system to manage on your own.
How It Works
Scope Your CUI
We identify where CUI lives and flows today, and determine the smallest environment that can contain it.
Choose & Deploy the Enclave
We help you select GCC High, PreVeil, or the Espresso Labs enclave, and deploy it around that scope.
Manage & Monitor It
We operate the enclave on your behalf, watching for configuration drift, access issues, and security events.
Map to Controls & Evidence
Everything the enclave does is mapped back to your controls, with evidence collected automatically for your GRC dashboard.
Real CUI Protection, Sized to Fit
A managed enclave gives small and mid-sized defense contractors the same protection larger primes rely on, without the enterprise budget.
3
Enclave options, matched to your budget and infrastructure
Managed
We configure, monitor, and maintain it, not just deploy it
Mapped
Every enclave control connected to your evidence and controls
CMMC Enclave Is Not the Whole Story
An enclave protects and isolates the systems that touch CUI, but CMMC Level 2 requires all 110 NIST SP 800-171 controls, not just secure storage and communication. Access control, configuration management, vulnerability management, incident response, audit logging, security awareness training, and continuous monitoring all still apply, inside the enclave and across the rest of your environment.
An enclave on its own leaves all of that work to you. Someone still has to configure it correctly, keep it configured correctly, and operate every other control CMMC requires.
The full solution: Comply
With the full Espresso Labs Comply offering, we don't just help you choose an enclave, we administer and monitor it on an ongoing basis, and provide the numerous other controls that make up a complete CMMC solution: endpoint protection, patching, MFA and access control, 24/7 monitoring, vulnerability scanning, security awareness training, and automated evidence collection, all tracked in the same GRC dashboard as the enclave itself.
CMMC Enclave FAQs
A Managed Enclave, Sized to Fit Your Budget
Get CUI protection without an enterprise-scale deployment, fully managed and mapped to your compliance program.
Talk to our team