Espresso Labs vs. Vanta and Drata
Vanta and Drata show you where you stand. Espresso Labs does the work — implementing, enforcing, monitoring, and remediating the controls behind your compliance.
A Dashboard Shows You Gaps. We Close Them.
Vanta and Drata are compliance monitoring platforms. They connect to the tools you already run, pull status through APIs, and give you a dashboard that shows where you stand against a framework like SOC 2, ISO 27001, or HIPAA. That visibility is genuinely useful — but it's the beginning of compliance, not the end of it.
Neither platform implements your controls, enforces them across your devices and users, or fixes anything when something drifts. When Vanta or Drata flags a failing check — an unencrypted disk, an inactive account, a missing patch — someone on your team still has to go implement the fix. The dashboard tells you what's wrong. It doesn't make it right.
Espresso Labs is not a dashboard. It's a fully managed service that operationalizes the controls themselves — implementing them, enforcing them continuously, monitoring your actual environment 24/7, and remediating deviations or incidents automatically or through our team. Compliance status isn't something we report on. It's a byproduct of the work we do every day.
What Vanta and Drata Actually Do
Vanta and Drata made their name replacing the old way of doing compliance: a shared spreadsheet tracking controls, owners, and evidence links by hand. That was a real improvement — planning and documenting a compliance program in a live platform instead of a static Excel sheet. Both platforms are excellent at what they're built for: centralizing compliance visibility and automating evidence collection for an audit. That typically includes:
- •Read-only integrations that pull status from your existing IT and security tools
- •A dashboard that maps passing and failing checks to framework requirements
- •Automated evidence collection and audit-ready reporting
- •Alerts when a connected system falls out of policy
What they assume is that you already have the underlying IT and security stack in place — and the team to configure it, enforce it, fix what breaks, and respond when something goes wrong. For companies with a mature internal team, that's a reasonable trade. For most SMBs, it means paying for a dashboard on top of a program that still has to be built.
What Espresso Labs Actually Does
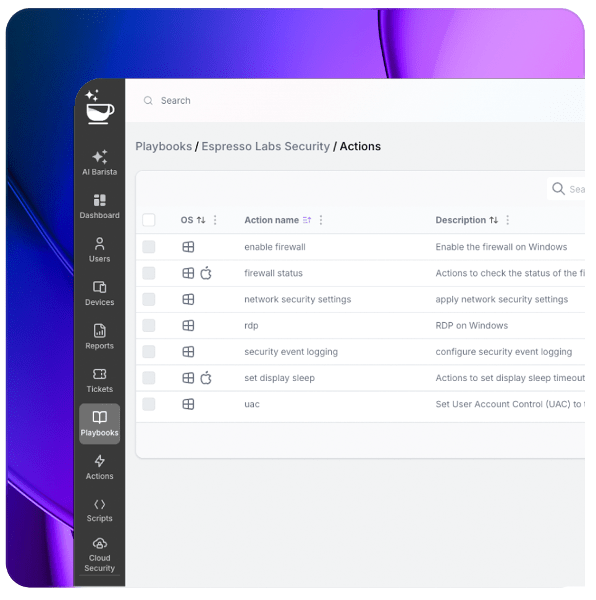
Espresso Labs is the IT, security, and compliance program itself — not a layer on top of one. Our AI-powered platform and team:
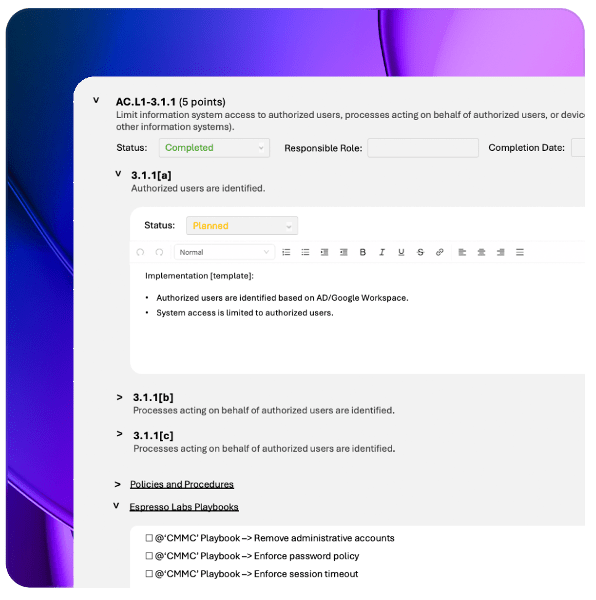
- •Implements the controls: device hardening, MFA, encryption, access control, patching
- •Enforces them continuously across every device and user, not just at audit time
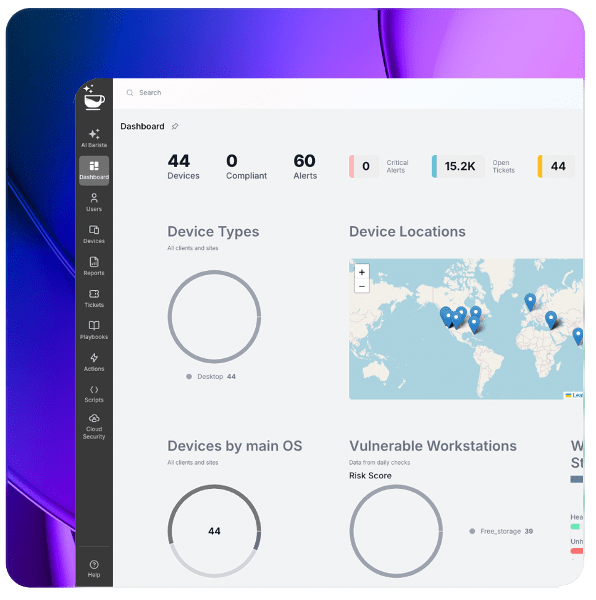
- •Monitors your real environment 24/7 — not just the status your tools report
- •Remediates drift and incidents automatically, or hands off to a human expert in seconds
Side-by-Side Comparison
Same goal — provable compliance. A different part of the problem: they give you visibility, we do the work.
| Capability | Vanta / Drata | Espresso Labs |
|---|---|---|
| What it is | Compliance monitoring dashboard (GRC platform) | Fully managed IT, security & compliance service |
| Control implementation | You build and configure the controls yourself | Espresso implements and configures the controls |
| Control enforcement | ✗ Visibility only — flags drift after it happens | ✓ Actively enforced in real time, across devices, users, and access |
| Monitoring | Pulls status from tools you already run, on a check-in schedule | 24/7 monitoring of your actual environment, not just tool status |
| Remediation | ✗ You fix every flagged issue manually | ✓ Issues remediated automatically or by our team |
| Incident response | ✗ Not included — bring your own IR plan and team | ✓ 24/7 incident response included |
| Underlying IT/security stack | ✗ BYO — EDR, MDM, SSO, backup, etc. required separately | ✓ Included and fully managed as part of the service |
| Team required | You still need IT/security staff to do the work | No internal IT or security team required |
| Audit evidence | Centralizes evidence pulled from your tools | Generated automatically as a byproduct of doing the work |
| Cost model | SaaS subscription + your tool stack + your labor | All-inclusive, predictable monthly fee |
| Best for | Companies with an existing security team wanting a GRC layer | SMBs who want compliance actually handled, not just tracked |
Which One Do You Actually Need?
A Dashboard Might Be Enough If
- •You already have a mature IT and security team implementing and maintaining controls
- •Your tool stack (EDR, MDM, SSO, backup) is already in place and well managed
- •You mainly need centralized visibility and audit evidence for a framework you already meet
- •You have staff available to respond every time a check fails
Espresso Labs Makes More Sense If
- ✓You're an SMB without a dedicated IT or security team
- ✓You want the controls implemented and enforced, not just tracked on a dashboard
- ✓You want deviations and incidents remediated automatically, not just flagged
- ✓You want one accountable vendor and one predictable monthly bill
Stop Tracking Compliance. Start Operationalizing It.
See what a fully managed compliance program looks like — not just a dashboard.
Talk to our team