Compliance as a Service: Get Audit-Ready Without the Overhead
Regulations don't care how small your team is. Whether you're chasing a government contract, responding to a customer security questionnaire, or avoiding a fine, the burden of proof falls on you. Espresso Labs takes that burden off your plate — turning complex regulatory requirements into automated, continuously enforced controls that run in the background while you focus on your business.
Not a GRC Tool. A Compliance Team.
Most businesses treat compliance as a one-time event, a checklist completed before an audit and forgotten until the next one. Controls drift, evidence goes uncollected, and employees fall out of training. By the time the auditor arrives, the team is scrambling.
Espresso Labs turns compliance into a continuous, automated process. Controls are enforced every day. Evidence is collected automatically. Your compliance posture is always current, not just on audit day.
With AI Barista, backed by our live human experts, you can answer them instantly — in plain language, backed by real data from your environment. No manual report pulls, no waiting on your IT team.
Example queries:
What's Included in Compliance Management
Compliance Playbooks
Pre-built playbooks for enforcing controls for CMMC, HIPAA, SOC 2, IRS WISP, PCI DSS, NIST 800-171 and more
Policy & Procedure Templates
Get started quickly with templates of policies, procedures, SSPs, and map them to actionable controls
Compliance Monitoring
Espresso Labs continuously monitors your cybersecurity and compliance posture and responds to incidents
Data Protection
Protect sensitive information through secure storage, encryption, access controls, and controlled data sharing
Security Training
Deliver security awareness training, track completion, and securely retain training records and attestations to support compliance and audit requirements
Device Management
Enforce security policies across endpoints, including patching, encryption, configuration management, and device monitoring, while maintaining evidence for compliance and audits
Endpoint Security & EDR
Deliver endpoint protection and EDR capabilities to identify suspicious activity, contain threats, maintain security visibility, and support compliance requirements
Vulnerability Scanning
Perform ongoing vulnerability assessments to detect security weaknesses, track remediation efforts, and maintain evidence for compliance and audit requirements

24/7 Security Operations Center
Round-the-clock monitoring by our AI platform and live security experts, triaging alerts and responding to threats at any hour so nothing waits until morning

Incident Response
Documented, tested incident response plans and hands-on support to contain and remediate incidents, meet reporting deadlines, and preserve the evidence auditors expect

Network and Cloud Monitoring
Continuous visibility across your network and cloud environments to detect misconfigurations, unauthorized access, and anomalous activity, with findings logged for compliance and audit requirements

AI Penetration Testing
AI-powered penetration testing that finds and validates exploitable weaknesses before an attacker does, with findings routed straight into remediation and retained as audit evidence

Automated Patching
Operating system and application patches deployed automatically across every device, closing known vulnerabilities on schedule and documenting each update for compliance and audit requirements

SDLC Monitoring
Monitor your software development lifecycle, including code repositories, pipelines, and access, to catch insecure changes and secrets early and keep development aligned with your compliance requirements
Evidence Collection
Espresso Labs automatically collects, stores, and retrieves audit-ready evidence for compliance and security assessments
End-to-end Compliance
Preparation
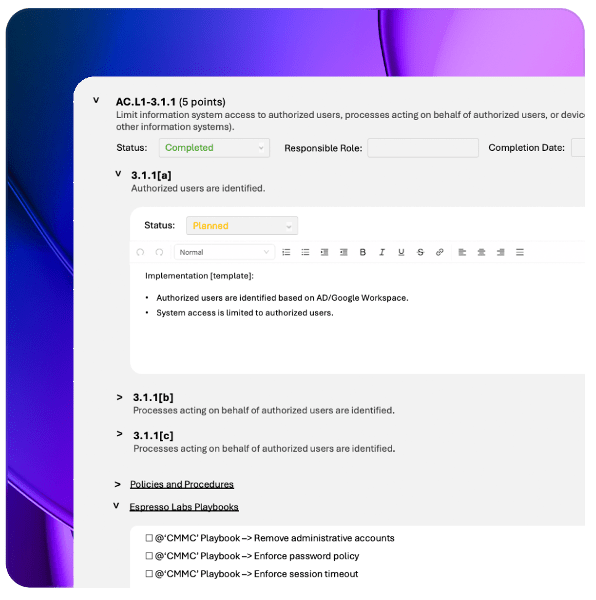
With Espresso Labs, you can quickly establish the IT and cybersecurity playbooks that form the foundation of your compliance program.
Our AI agent, built specifically for IT, security, and compliance operations, helps define policies, map them to required controls, and guide your organization through implementation.
Instead of spending months translating regulatory frameworks into operational policies, Espresso helps you:
- •Define required security policies
- •Map policies to required controls
- •Build a structured compliance program
- •Establish secure baseline configurations
- •Create documentation required for auditors
Enforcement
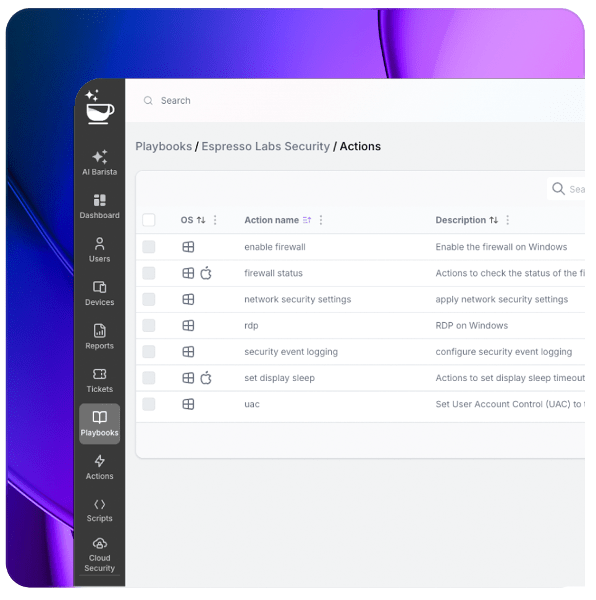
Compliance is not just documentation — it requires actual enforcement of technical controls across devices, users, and systems.
Espresso Labs automatically deploys and manages the tools and playbooks required to enforce your compliance controls, including:
- •Device security configurations
- •Endpoint protection and monitoring
- •Encryption and data protection
- •Patch and vulnerability management
- •Backup and recovery protections
We don't simply provide guidance. We deploy, operate, and maintain the controls on your behalf.
Monitoring & Triage
Compliance frameworks require continuous oversight, not a one-time setup.
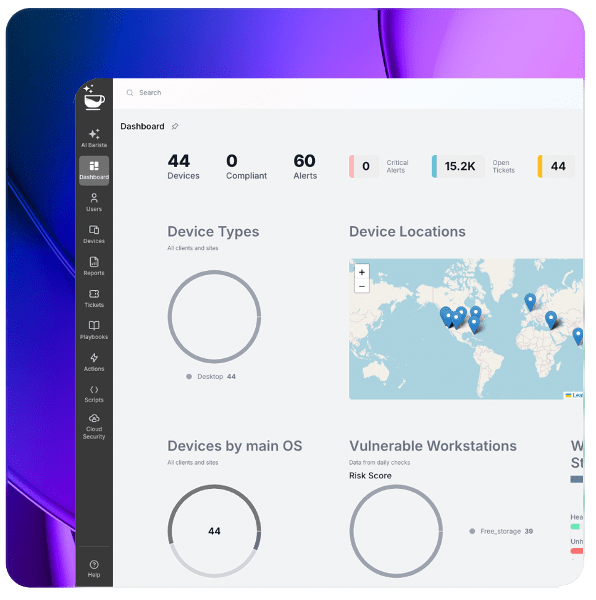
Espresso Labs continuously monitors your environment to ensure controls remain active and effective. If something drifts out of compliance — a device falls behind on patches, encryption is disabled, or an unauthorized configuration change occurs — Espresso detects and responds automatically.
- •24/7 monitoring of devices and users
- •Continuous compliance verification
- •Threat detection and response
- •Configuration drift detection
- •Automated remediation workflows
Evidence Collection & Assessment
When it's time to demonstrate compliance, Espresso Labs simplifies the process dramatically.
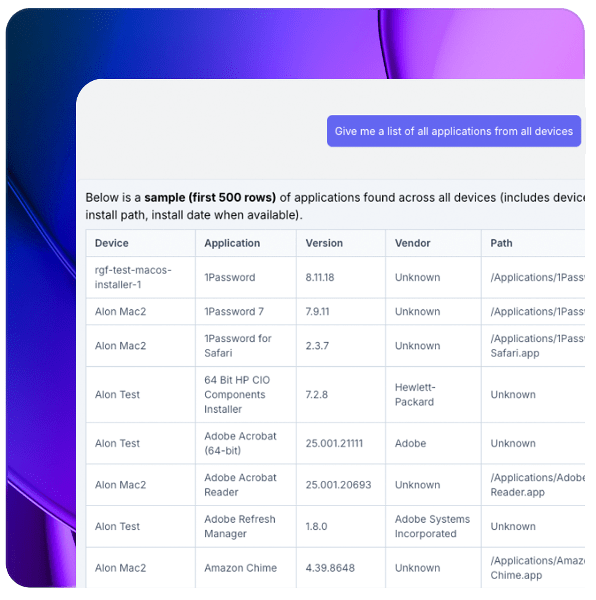
Instead of manually gathering logs, reports, and documentation, you can simply ask:
- •"Barista, are all my devices patched?"
- •"Barista, show encryption status across endpoints."
- •"Barista, generate device inventory for the auditor."
Espresso also continuously collects and organizes compliance evidence, including system configuration records, device inventories, patch and vulnerability reports, access logs, and policy documentation — creating a living compliance record ready for audits.
Start Your Compliance Journey Without the Complexity
Achieving and maintaining compliance frameworks such as CMMC, SOC 2, or ISO 27001 no longer requires a large internal team, months of preparation, or hundreds of thousands of dollars in consulting and tooling.
Espresso Labs replaces fragmented tools, manual processes, and expensive consultants with a single automated platform and managed service that defines, enforces, monitors, and maintains your compliance environment continuously.
Whether you are preparing for your first CMMC assessment or struggling to maintain ongoing compliance, Espresso Labs can help you dramatically reduce the time, cost, and operational burden.
Let Espresso handle the heavy lifting so your team can focus on running the business.
Compliance as a Service FAQs
Audit season shouldn't be a fire drill.
Schedule a demo today and see how Espresso Labs simplifies compliance.
Talk to one of our Compliance experts